
DNS is both the address book and the traffic plan of the internet. It translates a name such as gigatech.nl into the services required by visitors, mail servers and certificate authorities. Many incidents that appear to be hosting failures actually begin with an incorrect record, an expired change or nameservers that do not serve the same zone.
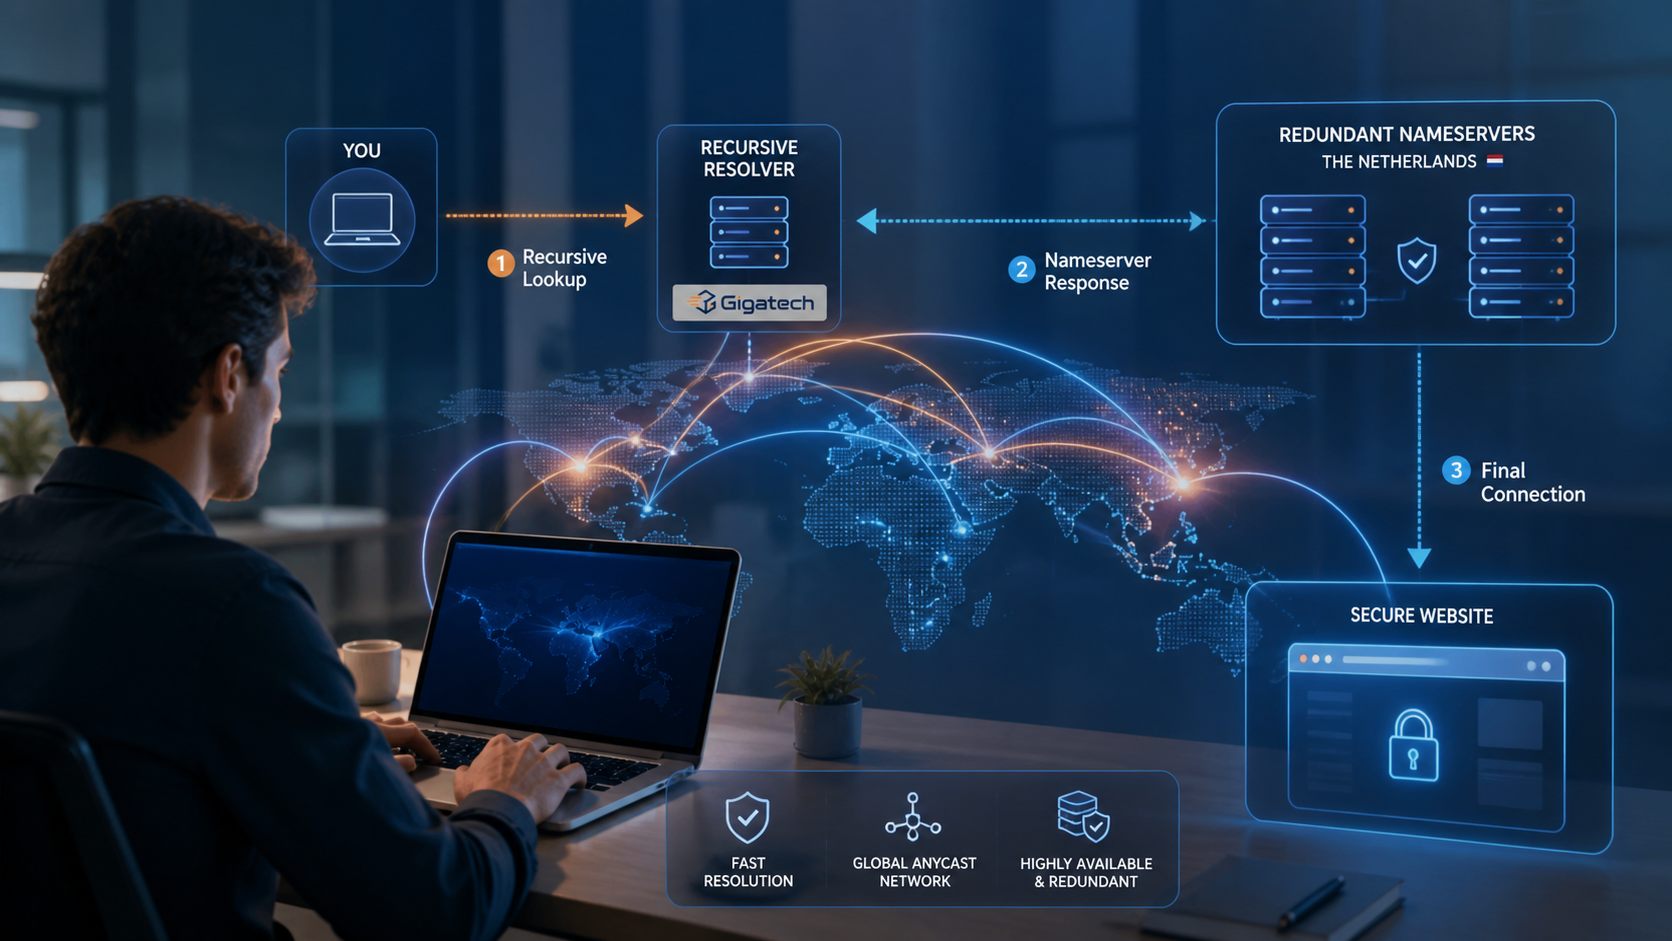
What happens when you open a domain?
The browser first asks a resolver which IP address belongs to the name. If the answer is cached, it is returned quickly. Otherwise, the resolver follows the DNS hierarchy to the domain’s authoritative nameservers. They provide the final answer from the DNS zone. Only then does the browser connect to the web server.
The most important DNS records
- A: connects a name to an IPv4 address.
- AAAA: connects a name to an IPv6 address.
- CNAME: points one hostname to another hostname.
- MX: specifies the servers receiving email for the domain.
- TXT: stores SPF, DKIM, DMARC and verification information.
- NS: identifies the authoritative nameservers.
- CAA: limits which certificate authorities may issue certificates.
- PTR: provides reverse DNS for an IP address and is particularly important for email.
Nameservers are not the same as DNS records
The registrar records which nameservers are responsible for the domain. The individual records live in the zone on those nameservers. Changing an A record at a provider that is not authoritative will therefore have no effect. Before making changes, verify where the active zone is actually managed.
TTL and propagation without the mystery
The TTL controls how long resolvers may cache an answer. After a change, old answers can remain until their TTL expires. Propagation is not one global switch slowly changing; it is a collection of caches with different remaining lifetimes. Lower the TTL well before a planned migration and return it to a sensible value after the move is stable.
Redundancy removes a fragile single point
Use at least two authoritative nameservers that are not dependent on exactly the same machine and network path. They must serve the same current zone. A second hostname that ultimately fails with the first provides little real resilience. Monitoring should test both reachability and the correctness of DNS answers.
DNSSEC verifies the authenticity of answers
DNSSEC signs DNS data so a validating resolver can check that the answer is authentic and unchanged. It does not encrypt traffic. An incorrect DS record at the registrar can make the domain unreachable, so key rotations and nameserver migrations require careful planning.
DNS during a migration
- Inventory every existing record, including verification records and subdomains.
- Lower the relevant TTL in advance.
- Build and test the new services before switching.
- Change only the required record or migrate the complete zone in a controlled way.
- Keep the old environment active while old caches may still point to it.
- Verify the website, email, SPF, DKIM, DMARC, certificates and third-party services.
For a complete move, see our guide to migrating a website without downtime or SEO loss. For mail authentication, read our guide to SPF, DKIM and DMARC.
Common mistakes
- Using a CNAME where other records must also exist.
- Removing the old MX record before mailboxes are synchronised.
- Adding a second SPF record instead of extending the existing one.
- Changing nameservers without copying the complete zone.
- Leaving DNSSEC active with keys that do not belong to the new provider.
Frequently asked questions
How long does a DNS change take?
It mainly depends on the previous TTL and existing caches. New queries may receive the new answer quickly while other resolvers temporarily continue to use the old one.
Can the website work while email does not?
Yes. The website and email use different records and services. A correct A record says nothing about MX, SPF, DKIM or the mailbox server.
Is more than one nameserver required?
Registries and good operational practice expect redundancy. More important than the number of names is that they reliably serve the same zone and do not all fail from one incident.
Unsure about a DNS zone? Have the changes reviewed before switching nameservers, mail or production IP addresses. Contact us through the Gigatech support portal.